
GitLab CVE-2026-110264 (CVSS 10): critical patch for self-managed installations
On 21 October 2026 GitLab fixed a maximum-severity flaw in its regular expression compiler that allows unauthenticated code execution. It affects every version since 7.0. Fixed versions, upgrade plan and detection.
On 21 October 2026 GitLab released a critical patch for seven lines of its product. The main fix, CVE-2026-110264, carries the maximum CVSS 3.1 score of 10.0: an integer overflow in the regular expression compiler allows, under certain conditions, an unauthenticated user to execute code on the GitLab server. It affects every Community and Enterprise edition since version 7.0. This article summarises the scope, the fixed-version table and an upgrade plan with verification.
GitLab strongly recommends upgrading all self-managed installations as soon as possible.
An explanation for readers who do not run servers
GitLab is where many companies keep the source code of their systems, run their build and deployment pipelines, and manage the credentials that reach production. A compromised GitLab server is therefore not an isolated incident: it gives access to the code, to deployment secrets and, from there, to other systems.
The flaw lets someone with no username or password run commands on the server. GitLab.com users have nothing to do, because GitLab has already fixed it. Organisations running GitLab on their own servers or cloud must upgrade.
Scope of CVE-2026-110264
According to GitLab's advisory, the defect is an integer overflow while compiling a specially crafted regular expression. Specialist outlets such as The Hacker News place the component in Onigmo, Ruby's regular expression engine, which GitLab ships and patches in its own packages. GitLab has not published the exact exploitation conditions, so exposure cannot be ruled out through configuration.
At the time of publication, GitLab reports no evidence of exploitation and the flaw is not in CISA's Known Exploited Vulnerabilities catalog. The same release fixes ten other vulnerabilities, two of them high severity: CVE-2026-15723 (8.2, OmniAuth-to-LDAP auto-linking) and CVE-2026-112212 (7.5, OAuth/OIDC discovery cache poisoning).
Fixed versions
| Installed line | Upgrade to |
|---|---|
| 19.5 | 19.5.1 |
| 19.4 | 19.4.3 |
| 19.3 | 19.3.6 |
| 19.2 | 19.2.9 |
| 19.1 | 19.1.9 |
| 19.0 | 19.0.10 |
| 7.0 to 18.11 | 18.11.13 or a newer line |
Versions 19.2.8, 19.3.5 and 19.4.2, which fixed a different flaw on 12 October, are still affected by this one. GitLab.com is already fixed, as is GitLab Dedicated from 19.3.5-internal0 or 19.4.2-internal0.
Upgrade plan
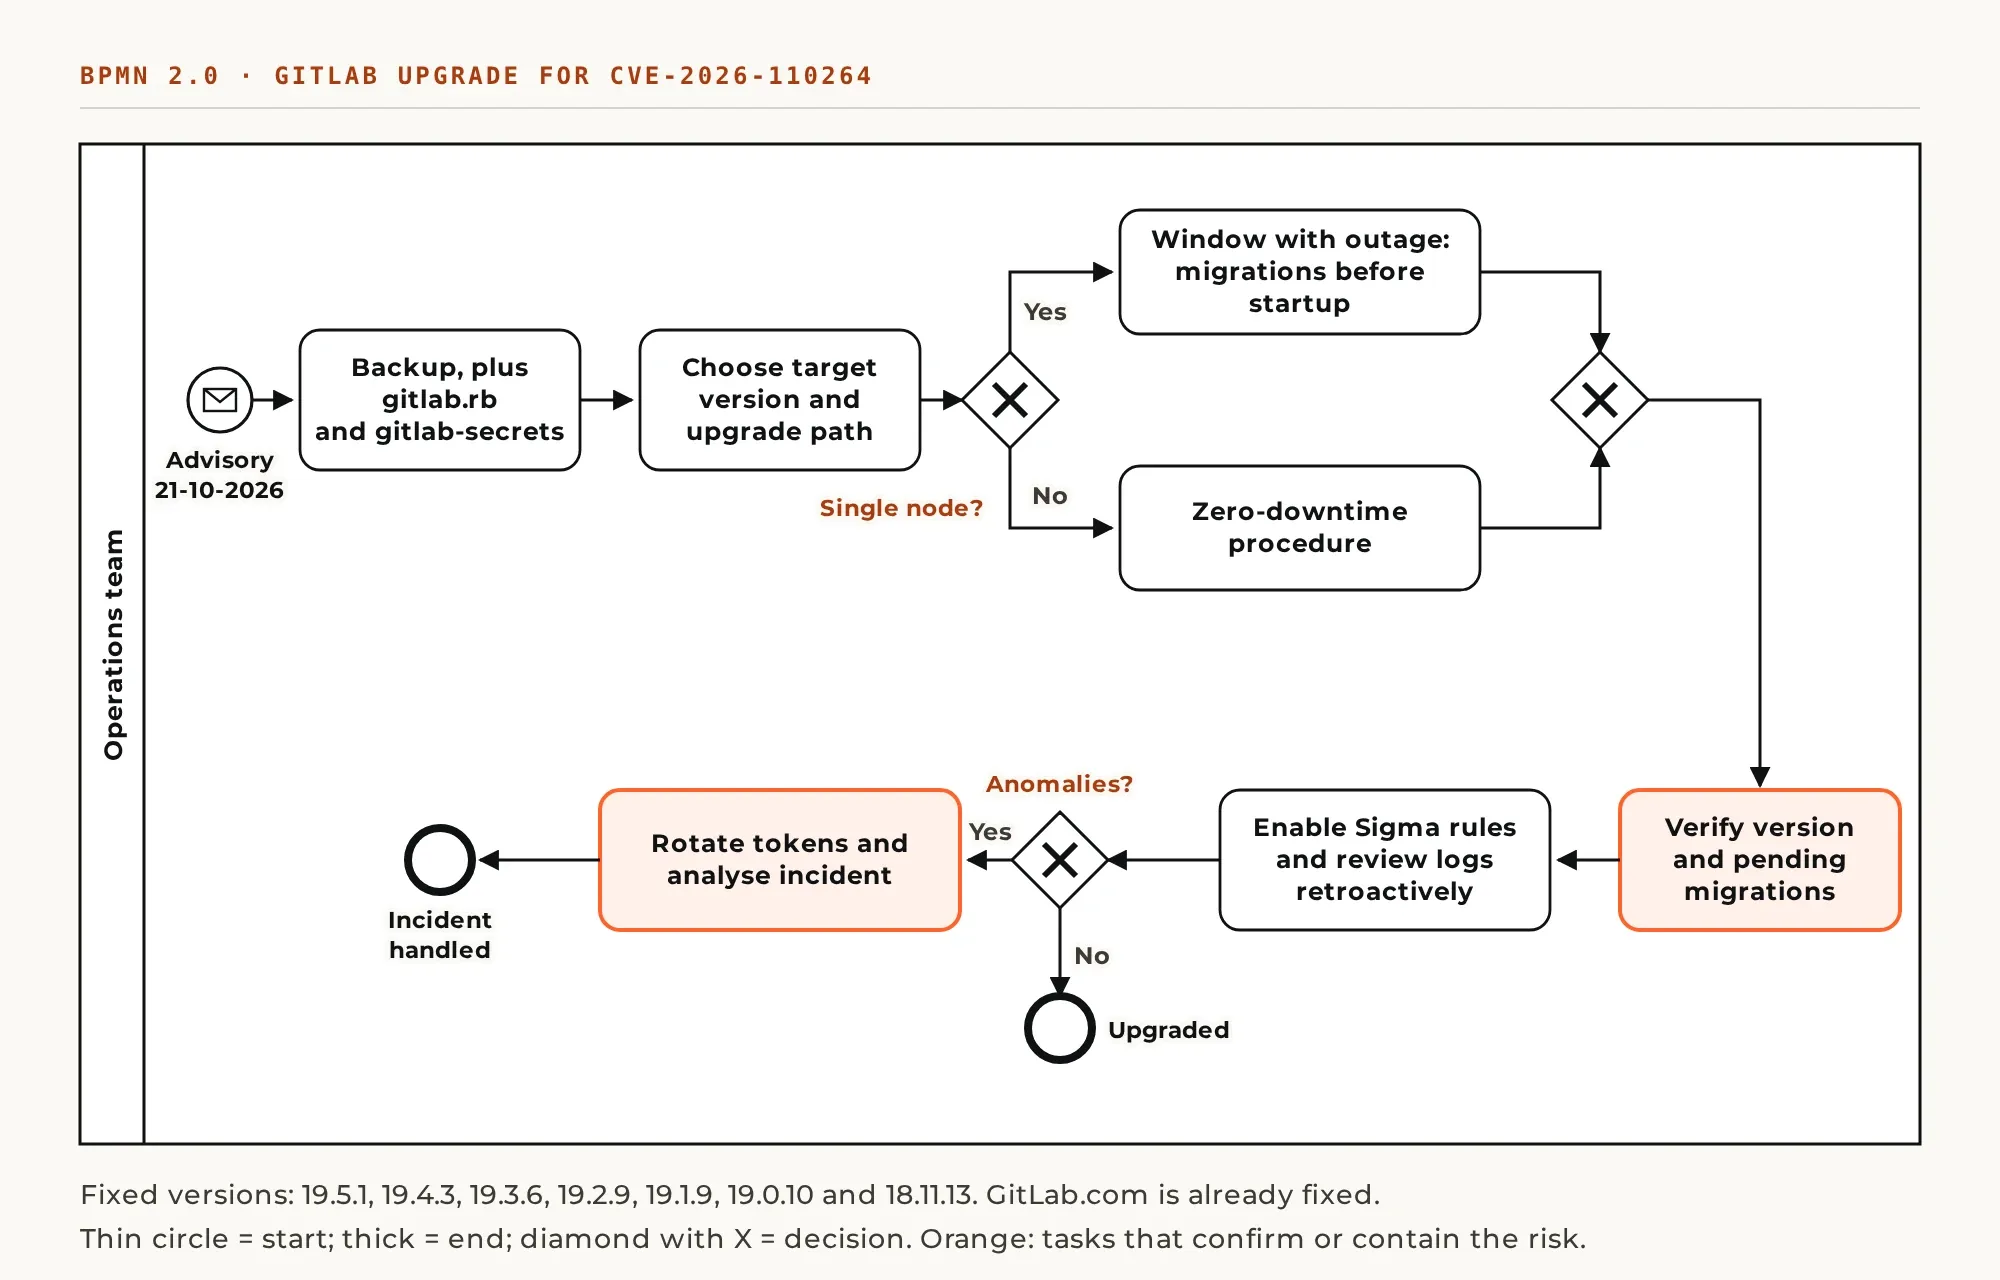
- Prior backup: run the GitLab backup and separately copy
gitlab.rbandgitlab-secrets.json, which the standard backup does not include. - Upgrade path: installations on old versions may need mandatory intermediate stops. The official upgrade path tool gives the sequence.
- Downtime: single-node installations will have an outage, because database migrations must finish before startup. Versions 19.4.3 and 19.3.6 include migrations, and 19.4.3 also a post-deployment one. Multi-node installations can follow the zero-downtime procedure.
- Runners: they are not part of this fix, but it is worth checking their tokens and versions in the same maintenance window.
Detection and verification
- Confirm the version under Admin > Overview > Dashboard or with
sudo gitlab-rake gitlab:env:info. - Check that migrations finished:
sudo gitlab-rake db:migrate:statusmust show no pending migrations. - Run
sudo gitlab-rake gitlab:check SANITIZE=trueto review overall health. - Enable the two Sigma rules GitLab published, "Onigmo native worker crash" and "Org mode render error burst", in the monitoring system or SIEM, and review logs retroactively for the days before the upgrade.
- If unexplained worker crashes or unrecognised administrative activity appear, treat it as an incident: rotate personal access, runner and deploy tokens, and review recent changes to repositories and CI variables.
Frequently asked questions
Our GitLab is only reachable through the VPN. Can we wait?
Restricting access reduces exposure, but any machine inside the private network can still reach it. With a 10.0 score and no published workaround, the recommendation is to upgrade in the next available window.
Does it affect GitLab Runner?
The advisory concerns the GitLab CE/EE server. Runners are not listed among the affected products.
Sources
- GitLab, Critical Patch Release: 19.5.1, 19.4.3, 19.3.6, 19.2.9, 19.1.9, 19.0.10, 18.11.13.
- The Hacker News, coverage of CVE-2026-110264.
Support upgrading GitLab
Xterra Engine plans and runs self-managed GitLab upgrades, with a verified backup, version path and post-upgrade checks. To request support or a quote, write to info@xterraengine.com or use the contact form.